DOT Hazardous Materials Security Plans: Applicability and Implementation
DOT Hazardous Materials Security Plans: Applicability and Implementation
Screen the materials and quantities in 49 CFR 172.800, assess risk, and implement personnel, unauthorized-access, and en-route security controls.
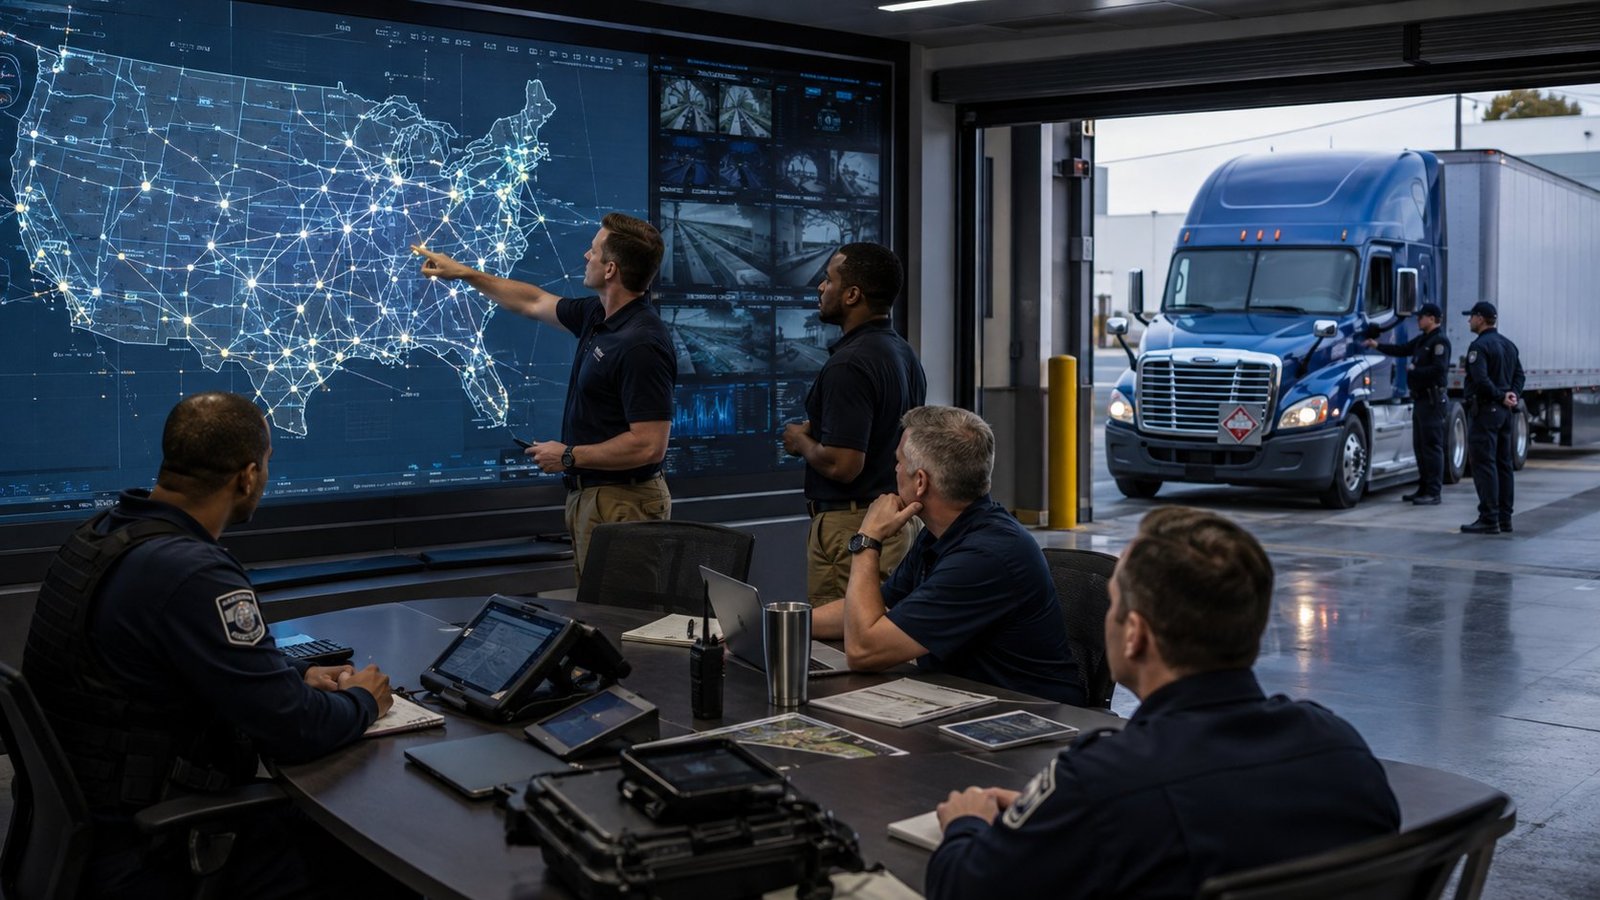
A person who offers or transports hazardous materials listed in 49 CFR 172.800(b) must develop and adhere to a written security plan meeting 172.802. Screen actual materials and shipment quantities, assess transportation risks, address personnel security, unauthorized access, and en-route security, train responsible employees, and review the plan at least annually.
Perform shipment-level applicability screening
Compare each material, hazard class, packing group, quantity, packaging, and conveyance with the current 172.800 list. Registration status alone should not replace the regulatory screen.
Assess realistic transportation risk
Evaluate facility access, staging, schedules, routes, stops, parking, tracking, communications, contractors, cyber systems, high-consequence targets, and credible misuse.
Build the three required elements
Address personnel security, prevention of unauthorized access, and en-route security. Assign senior management responsibility, define duties, and retain current implementing procedures without exposing sensitive details unnecessarily.
Worked example: large bulk shipment
A shipper identifies a covered large bulk quantity, verifies driver and carrier controls, restricts staging access, sets route and communication expectations, defines loss-of-contact escalation, and documents employee in-depth security training.
Review and exercise the plan
Review at least annually and after material, route, threat, facility, contractor, incident, or regulatory changes. Test contacts and response decisions with focused exercises.
Put the requirement into daily work
Assign an accountable owner and translate the DOT hazardous materials security plan decision into a field standard. Identify who performs each step, who reviews exceptions, what training and equipment are required, and where evidence is retained. Test the workflow with a real facility example before broad use.
Connect environmental, operations, maintenance, laboratory, purchasing, shipping, emergency-response, and contractor roles where their decisions affect the outcome. Use clear acceptance criteria so the same facts produce the same decision.
Records and reevaluation triggers
Keep the current regulatory basis, facility analysis, approvals, operating records, and exception history under a stable identifier. A reviewer should be able to reconstruct what was known, who decided, how the control was implemented, and how ongoing performance was verified.
Reevaluate after changes in material, process, equipment, quantity, storage, handling, vendor, destination, permit, law, incident, inspection finding, analytical result, or recurring failure. Document both the trigger and the resulting decision.
Common mistakes
- Assuming every placarded load requires a plan.
- Using PHMSA registration as the only applicability test.
- Writing a generic plan without shipment risks.
- Forgetting in-depth security training.
- Publishing sensitive routing or access details broadly.
Field checklist
- Screen materials and quantities under 172.800.
- Document the risk assessment.
- Address all three required plan elements.
- Assign senior management responsibility.
- Train employees with plan duties.
- Review annually and after changes.
Frequently asked questions
Does every hazardous waste shipment require a security plan?
What must the plan cover?
Should the plan be public?
Check your state rules
Authorized states may be more stringent, broader in scope, or use different adoption and reporting rules. Verify current requirements and agency interpretations in every applicable jurisdiction.
Primary sources
- 49 CFR 172.800 – Security plan applicability
- 49 CFR 172.802 – Security plan components
- PHMSA – Hazardous Materials Safety and Security
Federal sources reviewed September 7, 2026. Verify the current text and the rules adopted in your jurisdiction before acting.
This article explains a general federal baseline. It is not a facility-specific determination or legal advice. Verify current federal, state, permit, and local requirements for your facts.